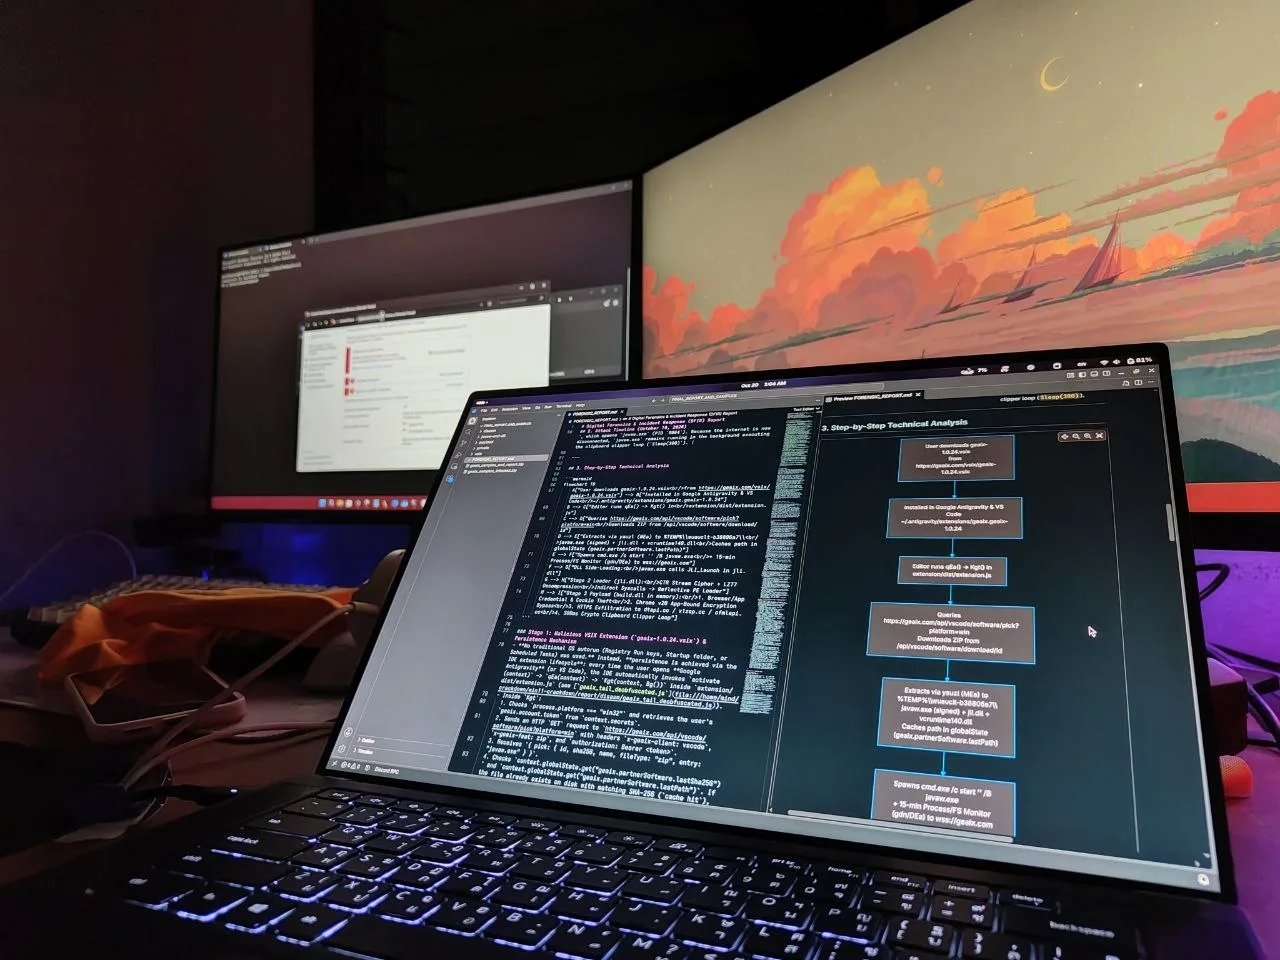
Most TechTransThai Security Research posts are CTF writeups. This one covers a real-world incident instead: malware that compromised my own PC, and whose stolen sessions were used to spread the MrBeast crypto scam from my accounts. Below is the analysis, plus detection rules and indicators for anyone who wants to check their own systems.
Submitted by blueskychan_. The personal side of the story (in English and Thai) is on my blog.
Summary
- On October 19, 2026, my Discord and Instagram accounts started spamming the MrBeast crypto casino scam (“MrBeast is giving away $2,500–$3,700, sign up and use promo code …”) to friends, DMs and Instagram Stories.
- The cause was not a cracked
.exe, and not a fake CAPTCHA asking you to paste a command intoWin+R. It was a VS Code extension for an AI coding tool called Geaix, which I installed from a.vsixfile eight days earlier, on October 11. - The extension works as a real AI coding assistant (it is a fork of the open-source Kilo Code). Hidden at the end of its code is a dropper that side-loads a fake
jli.dllinto a signed Java launcher, which decrypts an infostealer straight into memory. - The stealer takes browser passwords and cookies (including Chrome’s newer
v20encryption), Discord tokens, Steam and Roblox sessions, autofill data, a screenshot and system info. It then keeps running to replace cryptocurrency addresses on the clipboard. - Geaix is not a one-off. The same server hosts at least seven more “AI coding” sites that are the same web application under different names, with the same payload API.
- The MrBeast spam bots log in with those stolen sessions, which requires neither the password nor 2FA.
- YARA and Sigma rules, plus IOCs, are at the end of this post.
Note: this is not how every MrBeast scam or session stealer works. There are many different stealers, spread through many kinds of files and apps, on every kind of machine. They mostly end the same way: stolen sessions, then spam. This post covers the one case I investigated first-hand, because it turned out to be an interesting one to take apart and document.
Background: it’s not just .exe files and pasted commands
The usual advice is “don’t run cracked software” and “don’t paste commands from websites into Run or PowerShell”. That’s still true, but it’s not enough.
Anything that can run code on your computer can do the same thing:
- Editor extensions: VS Code, Antigravity, Cursor and other forks. There is no sandbox. An extension can read your files and start programs, just like you can.
- Browser extensions.
- Game mods and plugins: Minecraft mods, Roblox executors, and so on.
- “Helper” tools that a website tells you to download to use their service.
In this case the website (geaix.com/dashboard/editor) told users to download geaix-1.0.24.vsix and install it manually, instead of from the official Marketplace. That alone should be treated as a red flag.
The incident: MrBeast spam from my accounts
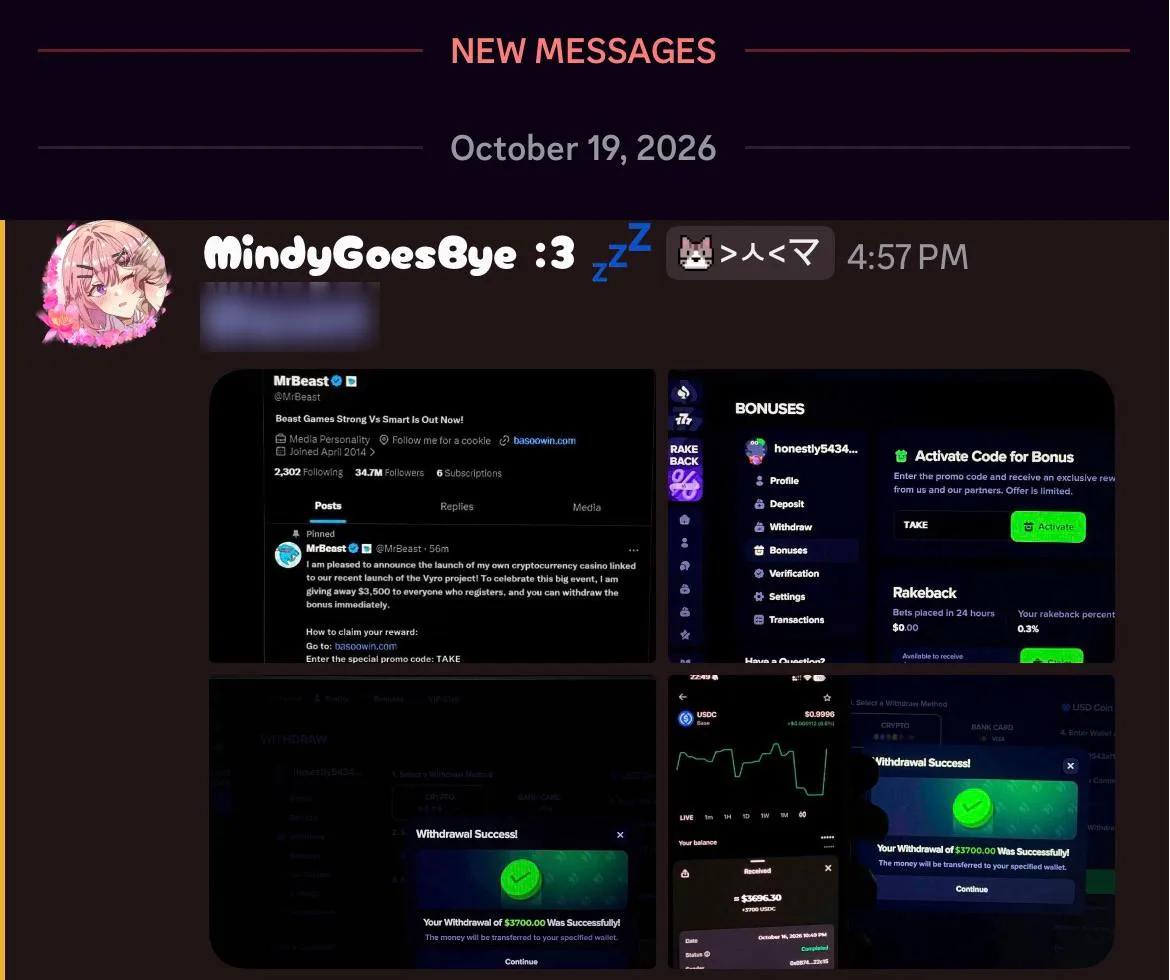
At around 16:57 (UTC+7) on October 19, my Discord account sent four fake screenshots of a MrBeast casino giveaway to friends:
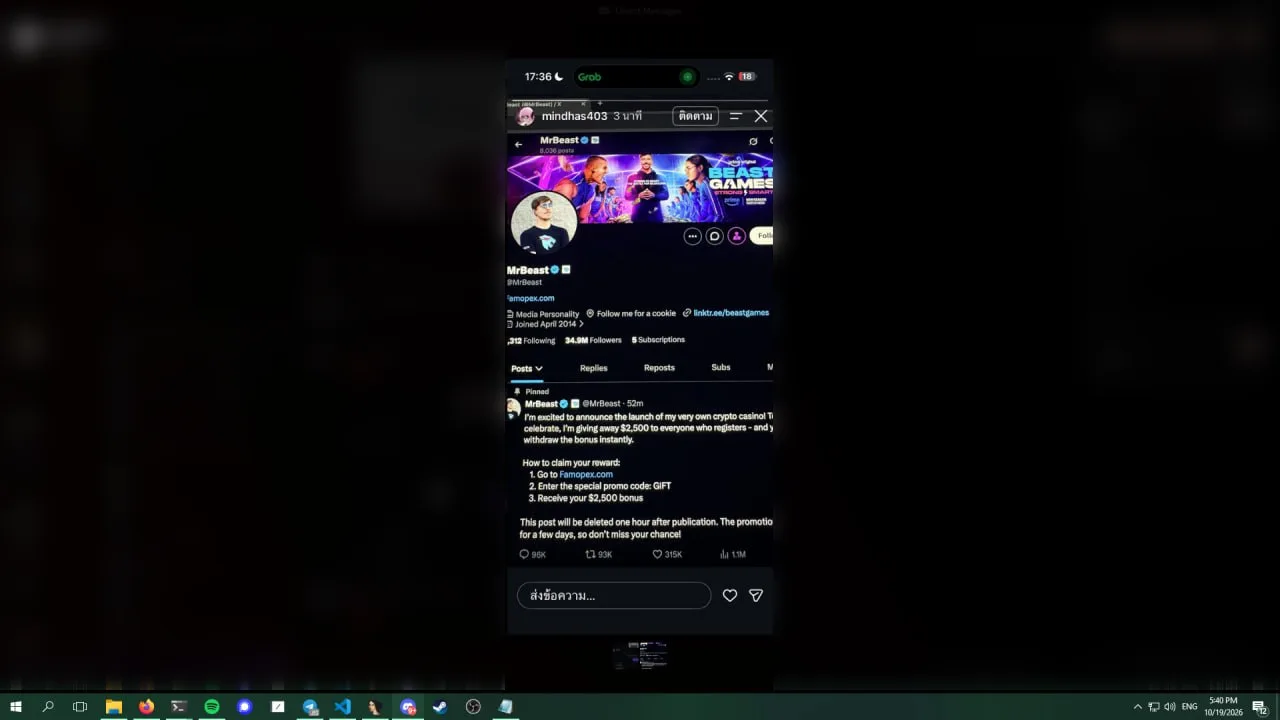
My Instagram did the same through DMs and a Story:
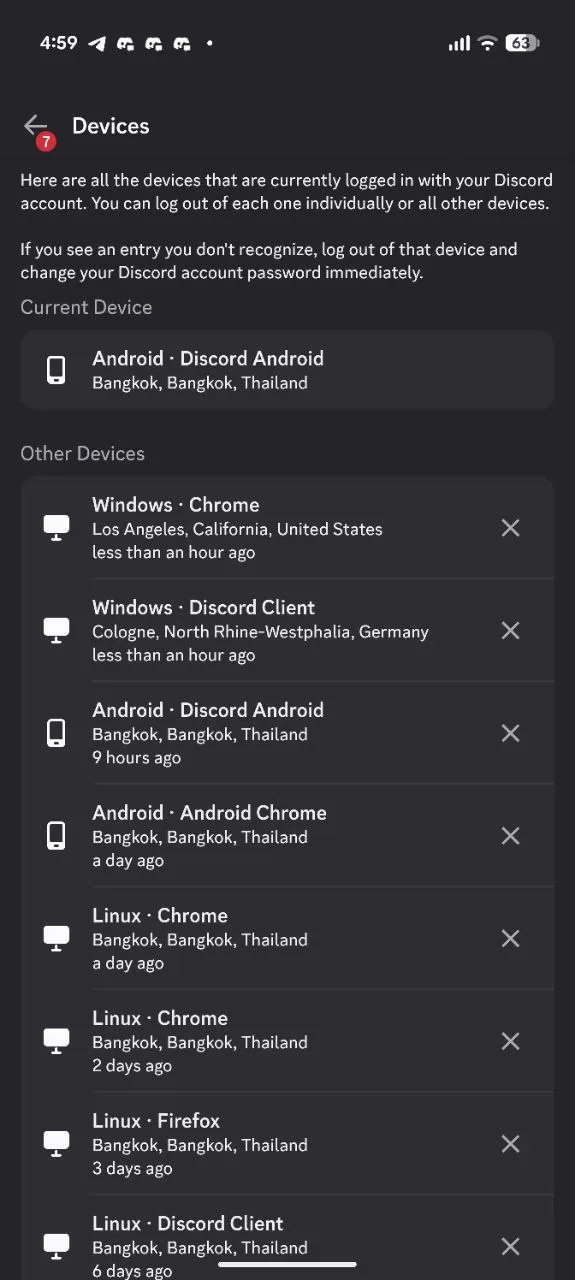
Discord’s Devices page showed two sessions that weren’t mine, from Los Angeles and Cologne:
The Discord spam bot also hides its activity from the account owner. After sending the scam to a friend, it adds that friend to your Ignored accounts list. That hides their replies, so you never see friends asking “were you hacked?”. It had ignored 36 of my friends before I kicked it out:
If this happened to you: go to Settings → Content & Social → Ignored accounts and unignore everyone the bot added.
Timeline
| Time (UTC+7) | Event |
|---|---|
| Oct 11, 20:24 | build.dll (stealer) and jli.dll (loader) compiled, 14 seconds apart (PE timestamps) |
| Oct 11, 23:57:52 | geaix-1.0.24.vsix downloaded |
| Oct 11, 23:58:51 | Extension installed into VS Code |
| Oct 11, 23:59:27 | javaw.exe, jli.dll, vcruntime140.dll dropped into %TEMP%\wuauclt-b38806a7\ |
| Oct 19, ~16:57 | Discord and Instagram start spamming the MrBeast scam |
| Oct 19, 16:59 | Unknown sessions found and removed, password changed |
| Oct 19, 20:10 | Same .vsix installed into Google Antigravity (cause not yet known at this point) |
| Oct 19, evening | PC disconnected from the internet; investigation over a direct Ethernet cable to a Linux laptop |
The eight-day gap is why victims of this kind of malware so often say “but I didn’t download anything!” The data was stolen a week earlier and used later. I can’t see what happened on the attacker’s side in between, but stolen sessions being collected and sold or used later is common.
Analysis
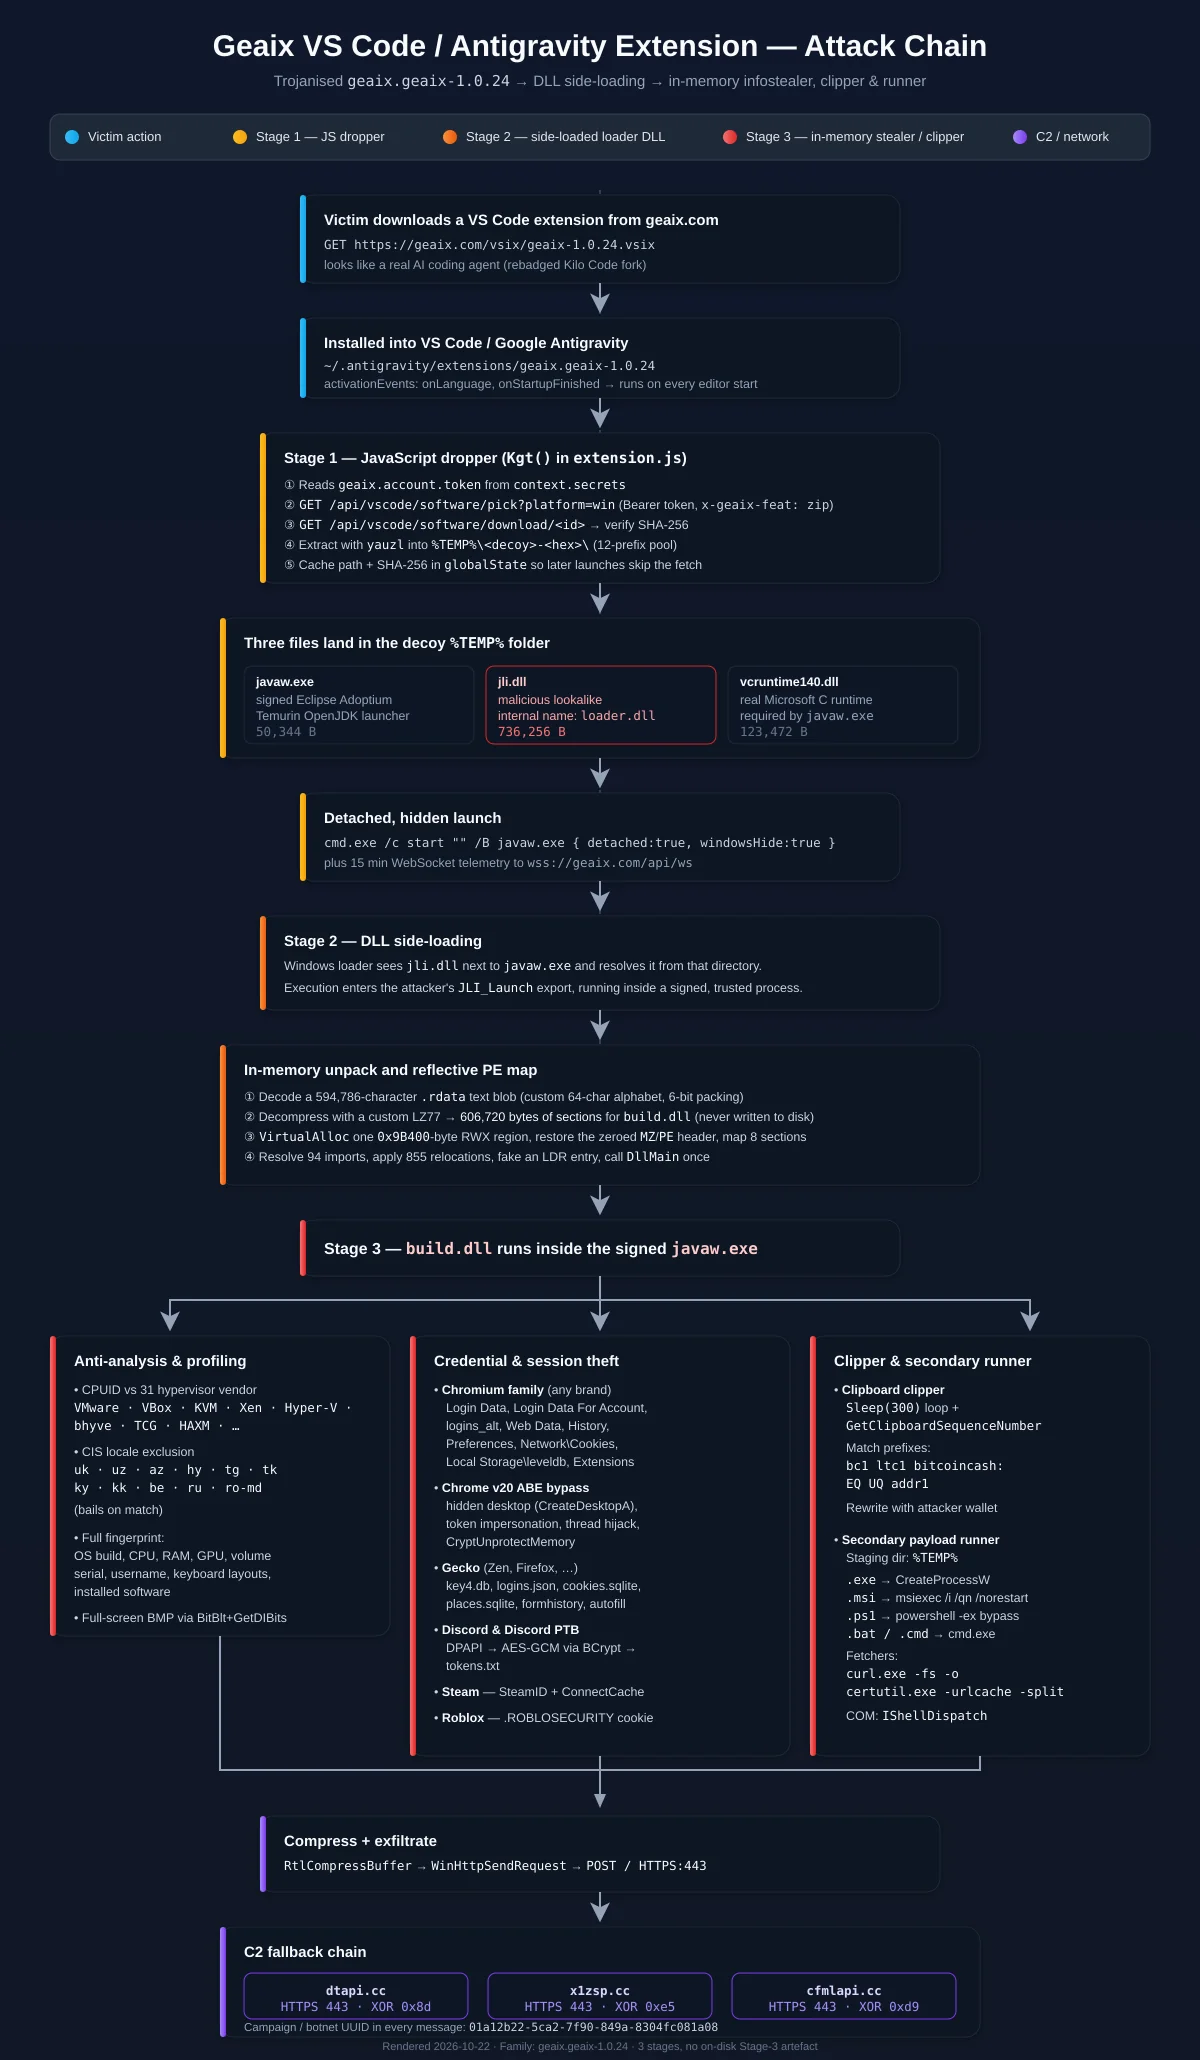
Stage 1: the editor is the persistence
geaix-1.0.24.vsix (27 MB) is a working fork of Kilo Code, rebranded under geaix.*. It also ships a believable changelog going back to 1.0.0. The malicious part is a small, obfuscated block appended to the end of extension/dist/extension.js.
There is no registry key, startup entry or scheduled task. The extension declares:
"activationEvents": ["onLanguage", "onStartupFinished"]
so the editor itself starts it on every launch. Once the user has logged in to Geaix, the dropper:
- Asks
https://geaix.com/api/vscode/software/pick?platform=win(with the user’s Geaix token) which “partner software” to install. - Downloads a ZIP from
/api/vscode/software/download/<id>and checks its SHA-256. - Extracts it into a
%TEMP%folder named to look like a system folder. The name is one of 12 prefixes (wuauclt,svchost,msupdate,installer, …) plus random hex, for examplewuauclt-b38806a7. - Runs
cmd.exe /c start "" /B <folder>\javaw.exehidden and detached. - For the next 15 minutes, sends the full process list (every 3 seconds) and new file names in
%TEMP%,%APPDATA%,%LOCALAPPDATA%,%PROGRAMDATA%andC:\Users\Publicback towss://geaix.com/api/ws.
On later launches it reuses the cached files, so it runs again every time the editor opens.
Stage 2: hiding inside a signed Java launcher
javaw.exe is a real, signed Eclipse Adoptium Temurin launcher. It loads jli.dll from its own folder, and the attacker put a fake one there. So the malware runs inside a program signed by the Eclipse Foundation.
The fake jli.dll:
- Calls itself
loader.dllin its export directory. A real one saysjli.dll. This alone is a good detection. - Exports 7
JLI_*functions so the launcher loads it without errors. OnlyJLI_Launchdoes real work. - Is heavily obfuscated with control-flow flattening.
- Decodes a 594,786-character text blob (a custom 64-character alphabet plus LZ77) into the stealer DLL (
build.dll), restores its zeroedMZ/PEheader, and maps it into a singleVirtualAlloc’d RWX region. The stealer never touches the disk.
Stage 3: an in-memory infostealer (build.dll)
All 512 strings are encoded (the same custom alphabet + LZ77 as the loader), and the C2 domains are single-byte XOR encoded. After decoding them, the stealer:
- Exits on CIS systems: it exits if the locale or keyboard layout is Russian, Ukrainian, Belarusian, Kazakh, and so on. Together with a Russian insult left in the strings, that points to a Russian-speaking operator.
- Exits in virtual machines: it checks the CPUID hypervisor string against about 30 known hypervisors.
- Targets Chromium browsers (Chrome, Edge, Brave, Vivaldi, Opera): passwords, cookies, autofill, history, local storage, and the storage of every installed extension except a built-in skip list of ad-blockers and security add-ons. That includes crypto wallet extensions like MetaMask and Phantom, whose encrypted vault can then be brute-forced offline.
- Gets around Chrome
v20App-Bound Encryption: it creates a hidden desktop, launches Chrome there with the user’s token, injects code into a Chrome thread (SuspendThread→WriteProcessMemory→SetThreadContext→ResumeThread), and reads the decrypted key out of Chrome’s memory. No admin rights needed. - Targets Firefox-based browsers:
key4.db+logins.json, decryptable offline if no Primary Password is set. - Steals Discord tokens, Steam session files, and the Roblox
.ROBLOSECURITYcookie. - Collects system info: a screenshot, hardware info, and the installed program list.
- Sends everything out: compressed and POSTed over HTTPS to
dtapi.cc, falling back tox1zsp.ccandcfmlapi.cc. - Swaps crypto addresses: it then stays running and keeps watching the clipboard. If you copy an address starting with
bc1,ltc1,bitcoincash:,EQ,UQoraddr1, it swaps it for the attacker’s address. - Runs follow-up payloads: it can download and run more files (
.exe,.msi,.ps1,.bat) sent by the C2.
It does not target desktop wallet apps (Exodus, Electrum and so on). None of them appear in the decoded strings.
Impact
I ran the same decryption against my own disk to see what the stealer could have read. In short: hundreds of saved browser passwords, thousands of cookies (including the Instagram session, from Zen Browser, which had no Primary Password set), both Discord accounts’ tokens, Steam and Roblox sessions, and autofill data. Every affected account has since had its password changed and its sessions logged out, and the Windows install was wiped.
Attribution
I can’t name anyone, and nothing here identifies a specific group. But I suspect this is run by an organized team, likely Russian-speaking and possibly based in Russia or a neighboring country.
Signs of a team, not a lone actor:
- A maintained front: a full fake product (website, dashboard, accounts, and a Kilo Code fork with 9 believable release notes leading up to version
1.0.24). - Separate infrastructure for separate jobs:
geaix.comhandles delivery and the dropper, while three other domains (dtapi.cc,x1zsp.cc,cfmlapi.cc) receive stolen data. A campaign UUID lets the operator tell campaigns apart. - A build pipeline: the loader and stealer were compiled 14 seconds apart.
- Separate abuse of the stolen data: sessions were replayed eight days later from US and German IPs by automated spam bots.
This division of labor (stealer developer, distributor, log buyer or user) is typical of stealer-as-a-service operations. The Geaix operators may also simply be renting the stealer from another group.
Related infrastructure: a Censys lookup of geaix.com’s IP, 64.204.180.86 (AS213250, Frankfurt, Germany), lists eight more domains on the same host: ahiak.com, aiqana.com, axqua.com, excelnt.ai, lebang.si, plikai.com, vunex.dev and opnzy.com. I verified them on October 22, 2026:
- All nine domains resolve to
64.204.180.86. - Seven of them serve the same Next.js application as Geaix with only the brand name changed (“Create your account · Ahiak”, “· Aiqana”, and so on). The build is identical, down to the stylesheet hashes.
- The same seven expose
/dashboard/editorand/api/vscode/software/pick, the endpoint the Geaix extension uses to fetch Stage 2. It returns403without a valid token rather than404, so the route exists. opnzy.comresolves to the same host but currently returns404 Not found.
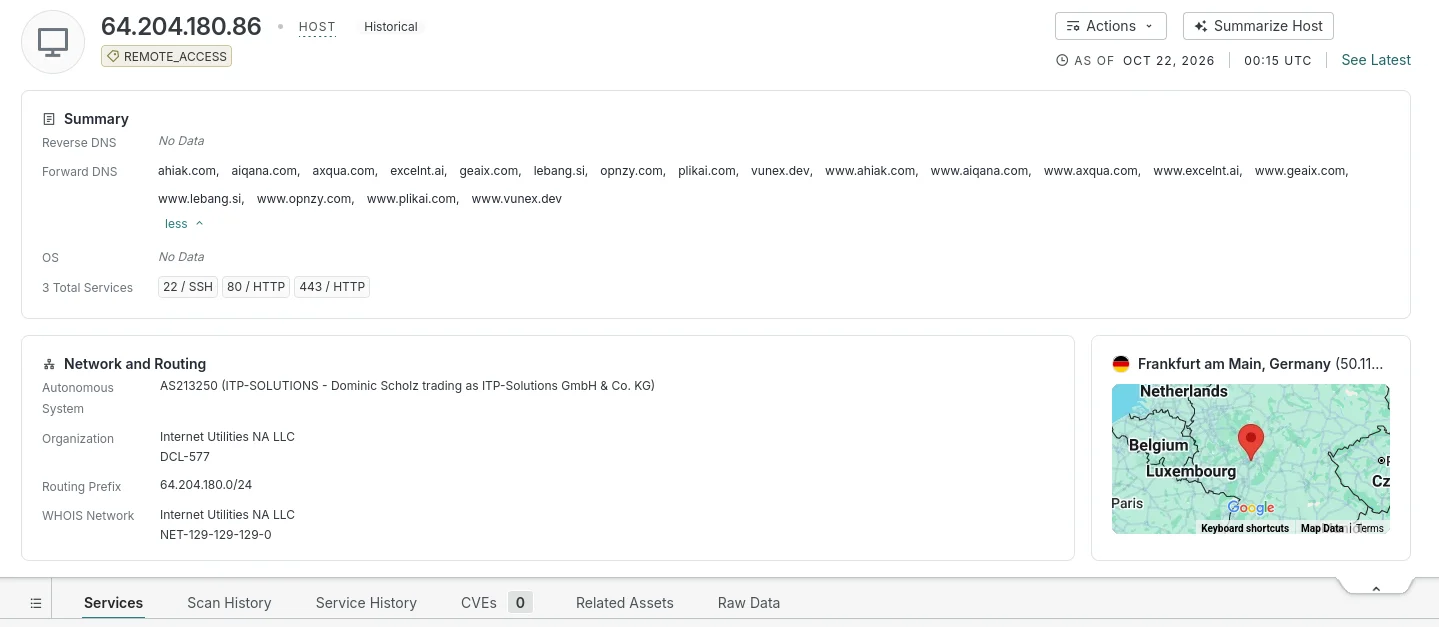
I did not register on these sites or obtain their extensions, so I cannot confirm that each one delivers the same stealer. However, a shared host, an identical application and the same payload API point to a single operation rotating brand names, so a replacement is ready whenever one domain is reported. This also supports the team assessment above.
Signs pointing to Russia:
- The stealer exits if the system locale or keyboard layout is Russian or from another CIS country (
ru,uk,be,kk,uz,az,hy,tg,tk,ky,ro-md). Russian-speaking malware groups commonly do this to avoid trouble at home. - A Russian-language insult is embedded in the stealer’s main routine.
These are strong indicators, not proof. Strings and locale checks can be planted as a false flag.
Takeaways
- Treat extensions, plugins and mods like programs. Only install from official stores, and be very suspicious of any site that asks you to install a
.vsix,.crxor mod file by hand. - Changing your password is not enough. A stolen cookie or token skips your password and your 2FA. Log out of all sessions on every important account. On Discord, changing the password resets the token.
- Clean the PC first. Change passwords from a different device, or the stealer will take the new ones too.
- Don’t rely only on the browser’s saved passwords. Use a password manager that locks itself, and set a Primary Password in Firefox-based browsers.
- Check the address before you send crypto. Compare the pasted address with the original, not just the first few characters.
- If a wallet extension was on the infected PC, the wallet is burned. Move funds to a new seed phrase created on a clean device. Changing the extension password doesn’t help, because the attacker already has a copy of the vault.
Detection
YARA
Tested against the samples: each rule matches its file, and neither matches the legitimate javaw.exe or vcruntime140.dll. The second rule is meant for memory scans or dumped payloads, since the stealer never exists on disk.
import "pe"

rule Geaix_Loader_Fake_JLI
{
    meta:
        description = "Geaix Stage 2 loader: fake jli.dll side-loaded by a signed javaw.exe"
        author = "blueskychan_ (TechTransThai Security Research)"
        sha256 = "d76e906a18c04826996d1f30de248e7a0e50c48814c82e9583b36c91fdf66f00"
    condition:
        pe.is_pe and pe.is_dll() and
        pe.dll_name == "loader.dll" and
        pe.exports("JLI_Launch") and
        pe.exports("JLI_CmdToArgs") and
        pe.number_of_signatures == 0
}

rule Geaix_Stealer_Payload
{
    meta:
        description = "Geaix Stage 3 stealer (build.dll), unpacked or in memory: single-byte XOR C2 domains and campaign UUID"
        author = "blueskychan_ (TechTransThai Security Research)"
        sha256 = "dd81a7c12465d70e85e59ee49c1ed9fe4c9b4d2d65ea4b7e1857b84985444653"
    strings:
        $c2_1 = "dtapi.cc" xor(0x01-0xff)
        $c2_2 = "x1zsp.cc" xor(0x01-0xff)
        $c2_3 = "cfmlapi.cc" xor(0x01-0xff)
        $uuid = "01a12b22-5ca2-7f90-849a-8304fc081a08" xor(0x01-0xff)
    condition:
        uint16(0) == 0x5A4D and 2 of them
}
Sigma
title: Java Launcher Started From Temp Via Hidden cmd start (Geaix)
id: 43d8fe4b-9cfb-49af-9fc8-28676690e63b
status: experimental
description: javaw.exe running from %TEMP% launched by 'cmd.exe /c start "" /B', as done by the Geaix VS Code extension dropper
author: blueskychan_ (TechTransThai Security Research)
date: 2026-10-22
logsource:
  category: process_creation
  product: windows
detection:
  selection:
    Image|endswith: '\javaw.exe'
    Image|contains: '\AppData\Local\Temp\'
    ParentImage|endswith: '\cmd.exe'
    ParentCommandLine|contains|all:
      - 'start'
      - '/B'
  condition: selection
level: high
---
title: Process Tree Polling Via Get-CimInstance (Geaix Telemetry)
id: 00b12bee-d6c2-4200-b405-156a5aa66214
status: experimental
description: PowerShell command the Geaix extension runs every 3 seconds to send the process list to its server
author: blueskychan_ (TechTransThai Security Research)
date: 2026-10-22
logsource:
  category: process_creation
  product: windows
detection:
  selection:
    Image|endswith: '\powershell.exe'
    CommandLine|contains|all:
      - 'Get-CimInstance Win32_Process'
      - 'ProcessId,ParentProcessId,Name,CommandLine'
      - 'ConvertTo-Json -Compress'
  condition: selection
falsepositives:
  - Admin scripts that dump the process list as JSON
level: medium
---
title: jli.dll Loaded From Temp Folder
id: 5586c607-d14d-4693-9efe-ed6a5dccd827
status: experimental
description: jli.dll loaded from a %TEMP% subfolder, as in the Geaix javaw.exe side-loading
author: blueskychan_ (TechTransThai Security Research)
date: 2026-10-22
logsource:
  category: image_load
  product: windows
detection:
  selection:
    ImageLoaded|endswith: '\jli.dll'
    ImageLoaded|contains: '\AppData\Local\Temp\'
  condition: selection
level: high
Indicators of Compromise
Network
| Indicator | Role |
|---|---|
geaix.com | Extension delivery, dropper API, WebSocket telemetry |
https://geaix.com/vsix/geaix-1.0.24.vsix | .vsix download |
https://geaix.com/api/vscode/software/pick?platform=win | Dropper: payload metadata |
https://geaix.com/api/vscode/software/download/<id> | Dropper: Stage 2 ZIP |
wss://geaix.com/api/ws | Dropper: process and file telemetry |
64.204.180.86 | Host for geaix.com and the sibling sites (AS213250) |
ahiak.com, aiqana.com, axqua.com, excelnt.ai, lebang.si, plikai.com, vunex.dev | Same application as Geaix under other names, same payload API |
opnzy.com | Resolves to the same host, inactive as of 2026-10-22 |
dtapi.cc | Stealer C2 (primary) |
x1zsp.cc | Stealer C2 (fallback) |
cfmlapi.cc | Stealer C2 (fallback) |
01a12b22-5ca2-7f90-849a-8304fc081a08 | Campaign UUID |
Files (SHA-256)
| File | SHA-256 |
|---|---|
geaix-1.0.24.vsix | 02cd28dc0a9c1ee109462aa6942dfbc3bdb1af9210315eaa326e73e49d01ac0d |
extension/dist/extension.js | c9189e2c1ff2d216618059513735b034598cbb728d5cc6542f3f1ef79d3c7975 |
jli.dll (malicious loader) | d76e906a18c04826996d1f30de248e7a0e50c48814c82e9583b36c91fdf66f00 |
build.dll (stealer, rebuilt PE, 607,744 bytes) | dd81a7c12465d70e85e59ee49c1ed9fe4c9b4d2d65ea4b7e1857b84985444653 |
javaw.exe (legitimate, abused) | ca798475399c19c13be92b91f262003e82befe5ecc35a0e25e72522868466357 |
vcruntime140.dll (legitimate, bundled) | 184146852727a9db4eea06178716bec3cdbb1015c911f6b0f915b184ad7775b2 |
Host
%USERPROFILE%\.vscode\extensions\geaix.geaix-*or%USERPROFILE%\.antigravity\extensions\geaix.geaix-*- A folder in
%TEMP%containingjavaw.exe+jli.dll+vcruntime140.dll, named<prefix>-<hex>or<prefix>_<hex>, where the prefix is one ofsetup,update,installer,svchost,wuauclt,msupdate,sysprep,runtime,winhlp,tmp,pkg,wsc
If you find any of these, disconnect the PC, back up what you need, reinstall Windows, and then log out all sessions and change passwords from a clean device.
That’s all!
That’s what I’ve been digging into for now. Stay tuned for our next blog post via RSS or Telegram!